Each finding: where it is, what it lets someone do, the fix, and its verdict and price to repair. Its evidence is in the appendix.
F1 Children's records are public
Critical Origin: Planted. Confirmed by: Live, signed out.
Where
-
drizzle/migrations/0004_children_public_read_demo.sql:2-5, table public.children. -
src/components/views/parent-view.tsx:42-49 reads it without a filter (see F8).
What it lets someone do
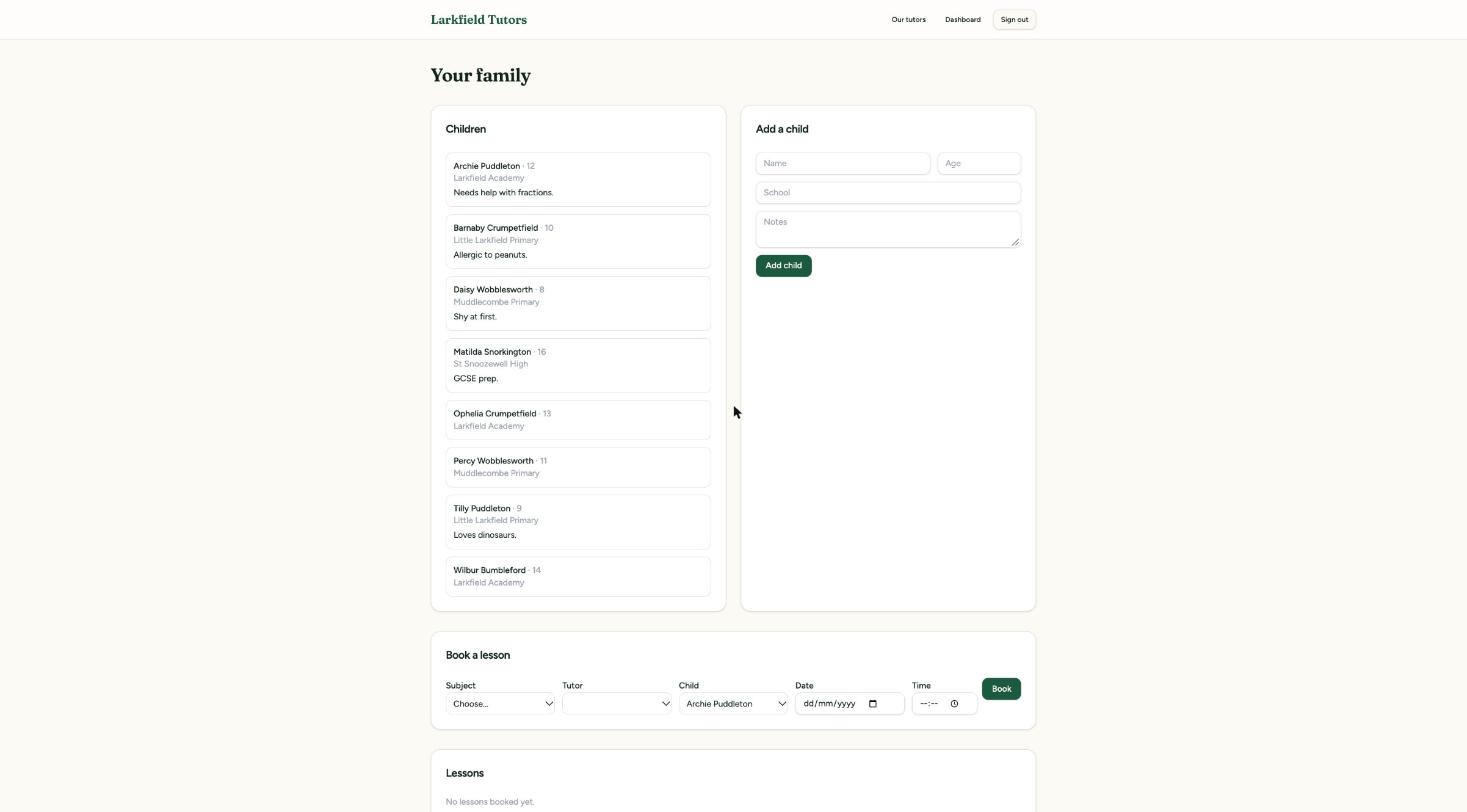
Anyone with the app's address can read every child's name, age, school and free-text notes, without an account. The publishable key that makes this possible is sent to every visitor's browser. Notes are written by parents and can hold health information: the seed data has "Allergic to peanuts."
Fix
Drop the demo rule and restore the original one, which already existed in 0000_larkfield_schema.sql:91-92: own children, admin, or a tutor with a booking for that child. Then run revoke select on public.children from anon;. Lovable manages this project's database schema, so ask Lovable to make the change.
Verdict: Patch. Price to repair: US$85.
See the evidence
F2 Every account's email is visible to every account
High Origin: Planted. Confirmed by: Live: Parent A read Parent B's.
Where
drizzle/migrations/0003_profiles_open_read_demo.sql:2-4, table public.profiles (id, email, full_name).
What it lets someone do
Anyone can sign up (sign-up is open; disable_signup: false) and then read the email address and name of every account, including staff and admins once those exist.
Fix
Restore the original rule, "own profile or admin" (0000_larkfield_schema.sql:79-80). Tutors already get parent contact details through the parents table, which is correctly restricted.
Verdict: Patch. Price to repair: US$65.
See the evidence
F3 Lesson notes are open to every account
High Origin: Planted. Confirmed by: Rule; no file existed to download.
Where
drizzle/migrations/0005_lesson_notes_open_read_demo.sql:2-5, storage bucket lesson-notes (private bucket, read rule open).
What it lets someone do
Any signed-in user can list every folder in the bucket and download any file in it. Folders are named after booking ids. The app's own screens stay tidy (the list of files shown to a parent comes from lesson_files, which is correctly limited to their bookings). But anyone calling storage directly could take every child's lesson notes.
Fix
Restore the booking-scoped read rule from 0001. Its check on public.bookings runs under the caller's own booking rules, so parents get their children's files, tutors get their lessons' files, and admins get everything.
Verdict: Patch. Price to repair: US$85 , including a retest with a tutor upload.
See the evidence
F4 "Pay now" takes no payment
High Origin: Planted. Confirmed by: Live: changed, then put back.
Where
-
src/components/views/parent-view.tsx:92-99 (mutation) and :241-243 (button). - Table
public.bookings, column paid, made writable by F6.
What it lets someone do
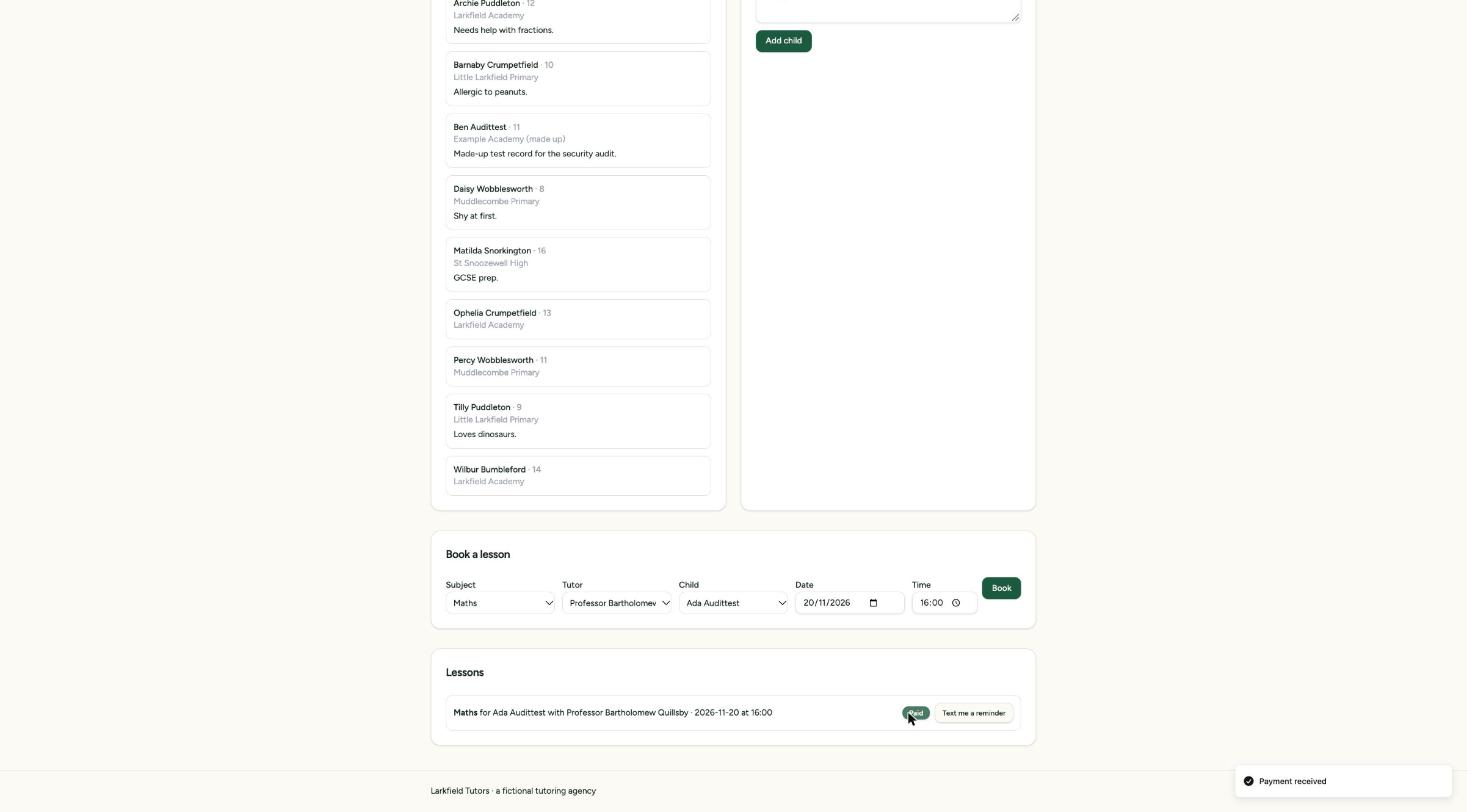
A parent can mark any of their own lessons as paid. The browser simply sets paid = true. No payment provider is involved and the server does no check. The agency would see "Paid" for a lesson nobody paid for.
Fix
- Take payment through a provider's hosted checkout.
- Have a server function receive the provider's confirmation and set
paid using the server-side key. - Remove the browser update, and stop parents writing
paid at all (see F6).
Verdict: Rework, as there is no payment system to repair. Price to repair: US$850.
See the evidence
F5 Keyboard trap in the booking date and time picker
High Origin: Planted. Confirmed by: Live.
Where
src/components/views/parent-view.tsx:189 (wrapper) and :264-278 (trapPickerFocus). WCAG 2.1.2 No Keyboard Trap (Level A).
What it lets someone do
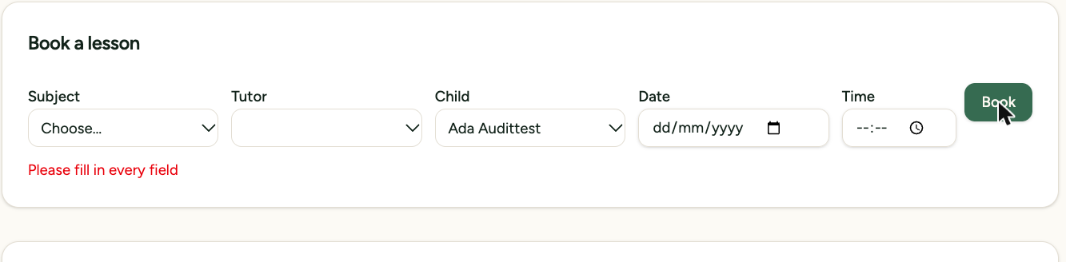
A keyboard-only user who reaches the date field can't Tab past it. Tab and Shift+Tab only swap between date and time, and Escape is swallowed. So they can't reach the Book button by Tab and can't leave the form.
Fix
Delete the handler and let the browser's normal Tab order apply.
Verdict: Patch. Price to repair: US$45.
See the evidence
F6 The booking-edit rule is open to every account
Medium Origin: Planted. Confirmed by: Rule; live cross-family edits blocked.
Where
drizzle/migrations/0002_bookings_open_update_demo.sql:2-4, table public.bookings.
What it lets someone do
The rule lets any signed-in user change any column of any booking, with no limit on the result. In practice Postgres applies the booking read rule to any update with a filter, to both the old row and the new one (PostgreSQL docs, CREATE POLICY). So a parent can only edit bookings they can already see: their own. Within those, nothing is checked. They can:
- mark the booking paid (F4)
- move it to another tutor
- change the subject to one that tutor doesn't teach
- move the date into the past
Any future widening of the booking read rule would immediately let everyone edit everyone's bookings.
Fix
- Restore the admin-only update rule (
0000_larkfield_schema.sql:102-103). - If parents should be able to reschedule, add a narrow rule for their own unpaid future bookings, plus column-level grants so only
lesson_date and lesson_time can change.
Verdict: Patch. Price to repair: US$130.
See the evidence
F7 The admin page has no role check
Medium Origin: Planted. Confirmed by: Live: both parents.
Where
-
src/routes/_authenticated/admin.tsx:4-19: there is no role check. The parent route src/routes/_authenticated/route.tsx:6-9 only checks that someone is signed in. - The menu link is hidden by
src/components/site-header.tsx:35-39.
What it lets someone do
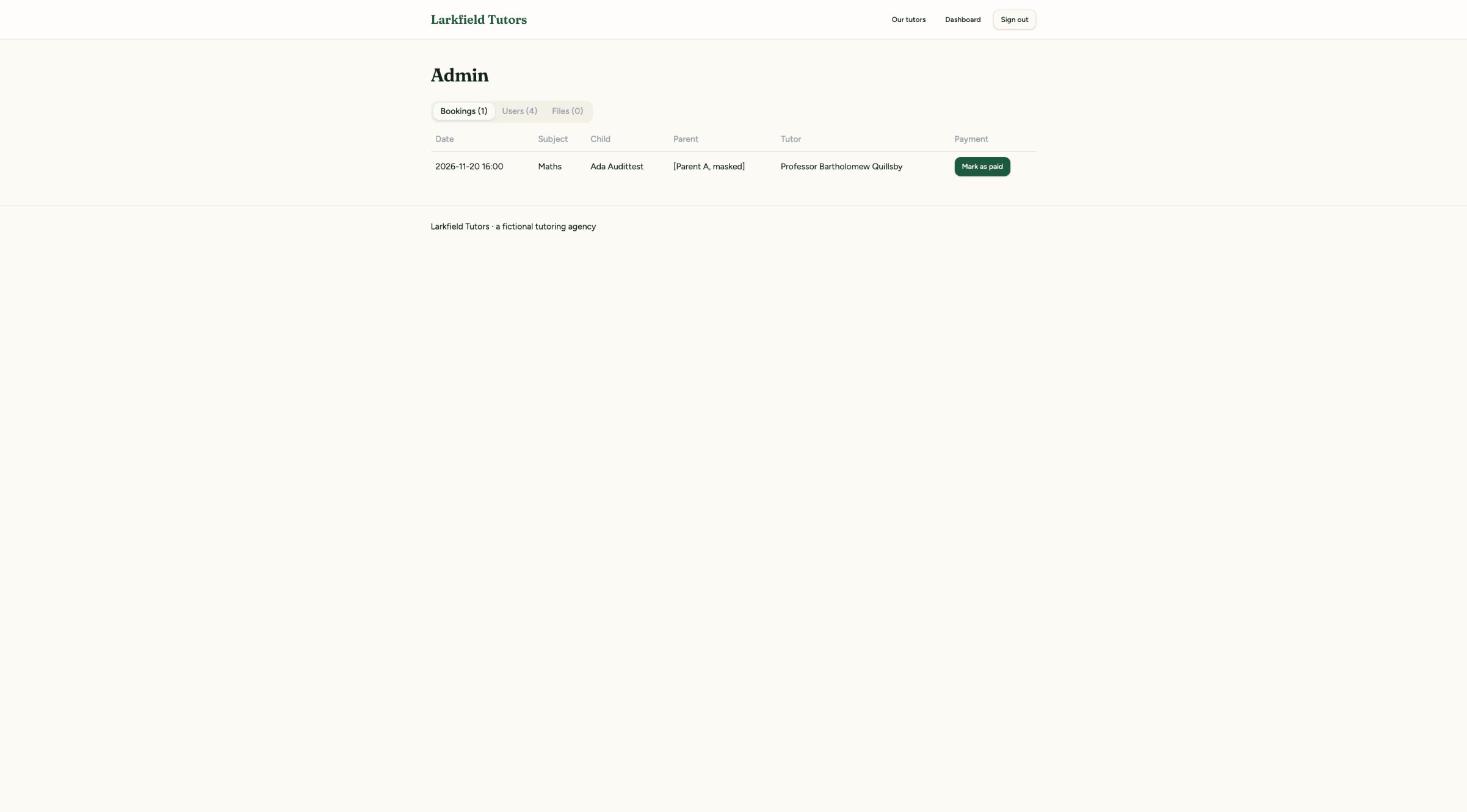
Any signed-in user who types /admin gets the admin screen with its Bookings, Users and Files tabs and "Mark as paid" buttons. What they see is still limited by the database rules: their own bookings, the tutors, and their own parent row. But the only protection left is the database. Hiding the link is not access control.
Fix
In the /admin route's beforeLoad, look up the caller's role and redirect anyone who isn't an admin. Keep the database rules as the real boundary.
Verdict: Patch. Price to repair: US$85.
See the evidence
F8 The parent dashboard shows other families' children
Medium Origin: New. Confirmed by: Live.
Where
src/components/views/parent-view.tsx:42-49 (query with no filter) and :184-187 (booking form "Child" list).
What it lets someone do
Every parent's "Your family" page lists every family's children, with schools and notes, and the booking form offers them as choices. A new parent with no children saw the eight seeded children. The booking form's default child was another family's (Archie Puddleton). A booking sent without changing it would be refused by the database and the parent would see a confusing error.
Fix
Filter by the parent's own id (.eq("parent_id", parent.data)). Fixing F1 also hides other families' children, but the query should not depend on that.
Verdict: Patch. Price to repair: US$45.
See the evidence
F9 Tutor email addresses are public
Medium Origin: New. Confirmed by: Live, signed out.
Where
-
drizzle/migrations/0000_larkfield_schema.sql:48 (grant select on public.tutors to anon, authenticated) and :84 (rule using (true)). - The public directory needs only five columns (
src/routes/tutors.tsx:26).
What it lets someone do
Anyone, signed out, can read every tutor's email address and the id of their sign-in account, not just the directory fields.
Fix
Grant column-level read on id, full_name, bio, subjects, hourly_rate only. Give the admin screen its emails through an admin-only function or view.
Verdict: Patch. Price to repair: US$130.
See the evidence
F10 Roles come from the email address
Medium Origin: New (design). Confirmed by: Code and auth settings.
Where
drizzle/migrations/0000_larkfield_schema.sql:114-141 (handle_new_user, run after insert on auth.users); :120 hard-codes the admin address.
What it lets someone do
The first account created with the seeded admin address becomes admin. An account created with a seeded tutor's or parent's address becomes that person and inherits their records, including a seeded parent's children. The role is granted when the account row is created, before the email is confirmed.
Today two things stop an outsider:
- Email confirmation is on (
mailer_autoconfirm: false). - The
.test addresses can't receive mail.
But anyone who creates the account on the Lovable Cloud Users page (which confirms automatically, as it did for the two test accounts) gets admin, or someone's records, at once. So does every sign-up, if confirmation is ever switched off.
Fix
- Remove the hard-coded admin address.
- Have an admin grant roles, for example through an invitation flow.
- Link a seeded record only after the email is confirmed.
Verdict: Rework. Price to repair: US$340.
See the evidence
F11 Sign-up and add-child fields have no labels
Medium Origin: Planted. Confirmed by: Live.
Where
-
src/routes/auth.tsx:90-102: "Parent sign up" fields fullName, email and password. -
src/components/views/parent-view.tsx:141-145: "Add a child" fields name, age, school and notes.
WCAG 1.3.1 and 3.3.2 (Level A).
What it lets someone do
Fields are identified only by placeholder text. The hint vanishes once someone types, and assistive technology gets no proper label. The sign-in form, by contrast, keeps its labels.
Fix
Add a visible <Label htmlFor=…> for each field.
Verdict: Patch. Price to repair: US$65.
See the evidence
F12 Booking form labels are not linked to their fields
Medium Origin: New. Confirmed by: Live.
Where
src/components/views/parent-view.tsx:280-282 (Field renders <Label> with no htmlFor) and :173-192. WCAG 1.3.1 and 4.1.2 (Level A).
What it lets someone do
The words Subject, Tutor, Child, Date and Time are on screen, but none is attached to its control. Screen readers announce "combo box" or "text field" with no name.
Fix
Give each control an id and pass it to Field as htmlFor.
Verdict: Patch. Price to repair: US$45.
See the evidence
F13 Grey helper text is too faint
Medium Origin: Planted. Confirmed by: Measured.
Where
src/styles.css:92 (--muted-foreground: #9CA3AF, used across the app) and src/routes/tutors.tsx:80 (subject badges). WCAG 1.4.3 (Level AA).
What it lets someone do
Helper text, schools, empty-state messages and tutor subject tags are hard to read for people with low vision, or on a bright screen.
Fix
A darker token such as #4B5563, which measures 7.24, 7.56 and 6.53:1 on the same three backgrounds.
Verdict: Patch. Price to repair: US$45.
See the evidence
F14 Focus jumps to the footer when the booking dialog closes
Medium Origin: Planted. Confirmed by: Live.
Where
src/components/views/parent-view.tsx:203-207 (onCloseAutoFocus sends focus to #site-footer). WCAG 2.4.3 (Level A).
What it lets someone do
After "Confirm booking" or "Cancel", keyboard and screen-reader users are dropped at the end of the page and have to find their way back.
Fix
Remove the override so the dialog returns focus to the element that opened it.
Verdict: Patch. Price to repair: US$20.
See the evidence
F15 Errors are silent for screen readers
Medium Origin: Planted. Confirmed by: Live.
Where
src/routes/auth.tsx:103 (sign-up error) and src/components/views/parent-view.tsx:197 (booking error). WCAG 4.1.3 (Level AA).
What it lets someone do
A blind user who submits an incomplete form hears nothing and doesn't know why it failed.
Fix
Add role="alert" to both error messages.
Verdict: Patch. Price to repair: US$45.
See the evidence
F16 Subject filters work only with a mouse
Medium Origin: New. Confirmed by: Live.
Where
src/routes/tutors.tsx:57-64. The filters are Badge elements (<div>) with onClick. WCAG 2.1.1 (Level A).
What it lets someone do
Keyboard users can't reach or use "All subjects", "Maths" and the other filters in the public tutor directory.
Fix
Render them as <button type="button" aria-pressed=…>.
Verdict: Patch. Price to repair: US$65.
See the evidence
F17 Known vulnerabilities in packages
Medium Origin: New. Confirmed by: bun audit.
Where
bun.lock.
What it lets someone do
Most of the 29 advisories affect tools that run only on a developer's machine or during the build. Two affect code that reaches visitors:
-
seroval 1.6.8: used by the router to pass server-rendered data to the browser. 2 moderate advisories about code or script injection through unusual data types; this app doesn't pass such types. -
zod 3.25.76: form validation in the browser. 1 high advisory about memory exhaustion on oversized collections; this app validates only small objects.
The single critical one, shell-quote via Lovable's development tools, runs only on a developer's machine.
Fix
Run bun audit fix (upgrades within the allowed ranges), update vite, vitest and the TanStack packages, rebuild, retest and re-run the audit.
Verdict: Patch. Price to repair: US$130.
See the evidence
F18 SMS key in the browser code
Low Origin: Planted. Confirmed by: Built bundle.
Where
src/lib/sms.ts:4-5 and :17-27; src/components/views/parent-view.tsx:101-105 and :244-254.
What it lets someone do
The reminder-service key LARKFIELD-SMS-KEY-demo-0001 is built into the code every visitor downloads. This key is fake, and the service it names (api.larkfield-sms.example) does not exist, which is why this is rated Low. With a real key this would be High: anyone could send texts at the agency's expense, or read its message history.
The "Text me a reminder" button also waits 0.6 seconds and shows "Reminder sent by text" without sending anything.
Fix
- Send reminders from a server function that reads the key from Lovable Secrets, and connect a real provider.
- Until then, remove the button or label it as a demo.
Verdict: Rework. Price to repair: US$255.
See the evidence
F19 Tutor photos have no text alternative
Low Origin: Planted. Confirmed by: Live.
Where
src/routes/tutors.tsx:72. WCAG 1.1.1 (Level A).
What it lets someone do
Screen readers announce an unnamed image on every tutor card. Some read out the long data: address instead.
Fix
alt="". The image only shows initials, and the tutor's name is next to it.
Verdict: Patch. Price to repair: US$20.
See the evidence
F20 Bookings are not checked on the server
Low Origin: New. Confirmed by: Code.
Where
-
drizzle/migrations/0000_larkfield_schema.sql:100-101: the insert rule checks only paid = false and that the child is the caller's. - The date check exists only in the browser, at
src/components/views/parent-view.tsx:19-23.
What it lets someone do
By calling the API directly, a parent can create bookings in the past, with a tutor for a subject that tutor doesn't teach, with any made-up subject text, or on a slot another family has already booked.
Fix
Check in the database that the date is today or later and that the subject is one of the tutor's, and add a unique rule on tutor, date and time.
Verdict: Patch. Price to repair: US$170.
See the evidence
F21 Success messages don't check the result
Low Origin: New. Confirmed by: Code.
Where
src/components/views/parent-view.tsx:92-98 and src/components/views/admin-view.tsx:49-56.
What it lets someone do
An update that the database rules quietly block still returns "no error", so the screen shows "Payment received" or flips the badge although nothing was saved. With the admin-only payment rule restored, a parent pressing "Pay now" would be told they had paid.
Fix
Ask for the updated row back (.select()) and treat zero rows as a failure.
Verdict: Patch. Price to repair: US$45.
See the evidence
F22 Database permissions are wider than the migration files say
Low Origin: New. Confirmed by: Live, signed out.
Where
-
drizzle/migrations/0000_larkfield_schema.sql:47-52: the grants written in the migration. -
:62-77: helper functions, which every caller may run by default.
What it lets someone do
The migrations grant signed-out visitors read access to tutors and (since 0004) children only. In practice they can query all seven tables and even send updates (tested on bookings). Every one of those calls is answered by the row rules alone. One mistaken rule written to public, or a table added without row rules, would be open to the whole internet.
Signed-out visitors can also call has_role(user_id, role). Combined with F2's list of account ids, anyone could find out which account is the admin.
Fix
Revoke table permissions the signed-out role doesn't need, and revoke execute on the helper functions from signed-out visitors.
Verdict: Patch. Price to repair: US$85.
See the evidence
F23 Upload checks happen only in the browser
Low Origin: New. Confirmed by: Code.
Where
-
src/components/views/tutor-view.tsx:25-33: PDF and 10 MB checks, browser only. -
drizzle/migrations/0001_lesson_notes_storage.sql:3-4: the upload rule checks only the folder. -
0000_larkfield_schema.sql:109-110: lesson_files.file_path is not tied to the booking's folder.
What it lets someone do
A tutor (or anyone holding a tutor account) can store files of any type and size under their bookings by calling storage directly. They can also register a file record pointing at a path in another booking's folder.
Fix
- Set the bucket's size limit and allowed types (
application/pdf, 10 MB). - Require
file_path to start with the booking id.
Verdict: Patch. Price to repair: US$85.
See the evidence
F24 No browser security headers
Low Origin: New. Confirmed by: Code; host not checked.
Where
src/start.ts and src/server.ts set no response headers. The build's .output/public/_headers sets only caching for /assets/*.
What it lets someone do
The app sends no content-security policy, no frame-ancestors or X-Frame-Options rule and no referrer policy. Another site could load it inside a frame to trick users into clicking (clickjacking). If a script-injection bug ever appeared, nothing would contain it. Session tokens are kept in browser storage (Supabase's default), so injected script could read them.
Fix
Add the headers in a server middleware and confirm them on the published host.
Verdict: Patch. Price to repair: US$85.
See the evidence
F25 Fonts load from Google
Low Origin: New. Confirmed by: Code.
Where
src/routes/__root.tsx:100-101.
What it lets someone do
Every page view sends the visitor's IP address, browser details and the referring page to Google's font servers. Google's font FAQ lists these. In 2022 a German court held that doing this without the visitor’s consent breached GDPR (LG München I, 3 O 17493/20).
Fix
Self-host Figtree and Fraunces. Both are under the SIL Open Font License.
Verdict: Patch. Price to repair: US$65.
See the evidence
F26 Names default to the email address
Low Origin: New. Confirmed by: Live: both test accounts.
Where
drizzle/migrations/0000_larkfield_schema.sql:119 and :135, which fall back to split_part(email,'@',1).
What it lets someone do
An account created without a name shows the part of its email before the @ as its name, in tutor screens, the admin page and the open profile list (F2). That is often enough to work out the full address.
Fix
Require a name at sign-up, or fall back to a neutral value.
Verdict: Patch. Price to repair: US$20.
See the evidence
F27 The local development server listens on the whole network
Low Origin: New. Confirmed by: Observed.
Where
Lovable's Vite settings, inherited through vite.config.ts and @lovable.dev/vite-tanstack-config.
What it lets someone do
vite dev printed two local-network addresses as well as localhost. Anyone on the same network can reach a developer's running copy, and the Vite development-server advisories in F17 apply to it.
Fix
Run local development with --host 127.0.0.1, or set it in the local config without changing the Lovable sandbox settings.
Verdict: Patch. Price to repair: US$20.
See the evidence